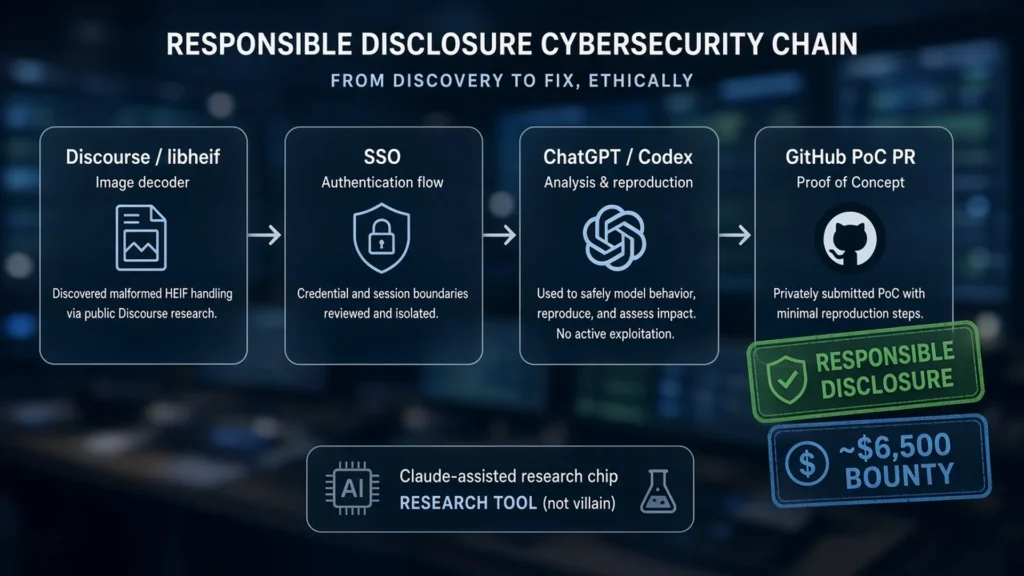
Indian security researchers at Hacktron used Anthropic’s Claude to help chain a Discourse/image-decoder bug with an OpenAI SSO misconfiguration, reach employee ChatGPT/Codex accounts and connected GitHub, then disclosed the path for a ~$6,500 bounty.
Independent security researchers at Hacktron used Anthropic’s Claude models to help build and adapt an exploit chain that reached OpenAI employee ChatGPT and Codex accounts and connected internal GitHub access, the Wall Street Journal reported. The team detailed the July 25, 2026 chain in its own technical write-up.
According to Hacktron, the path combined remote code execution on OpenAI’s Discourse-hosted community forum via a vulnerable libheif image-decoder path in Discourse image uploads, then an OpenAI single sign-on misconfiguration that turned forum compromise into ChatGPT/Codex account takeover for users who had signed in. With an employee Codex account connected to OpenAI’s GitHub organization, the researchers said they demonstrated impact by prompting Codex to open a harmless pull request in an internal monorepo without reading sensitive source, then stopped testing.
Hacktron said it reported the issues to OpenAI and Discourse, coordinated fixes, and received a $6,500 bounty from OpenAI. OpenAI clarified that the award recognizes the OpenAI-side finding; testing against the Discourse-hosted community forum was excluded from its bug-bounty program scope. Discourse published an advisory and patched the image-processing path. OpenAI fixed the SSO issue roughly 14 hours after the initial submission, Hacktron said.
The episode is responsible-disclosure research, not a claim that Anthropic or OpenAI intentionally enabled the intrusion. It lands in a broader debate about how frontier models lower the expertise and time needed to weaponize software bugs, while also showing how bug-bounty programs and fast patches can contain disclosed chains.
This brief covers the attributed Hacktron disclosure and WSJ account. It does not dunk on either lab and does not equate the case with unrelated agent breakout stories already on the site.