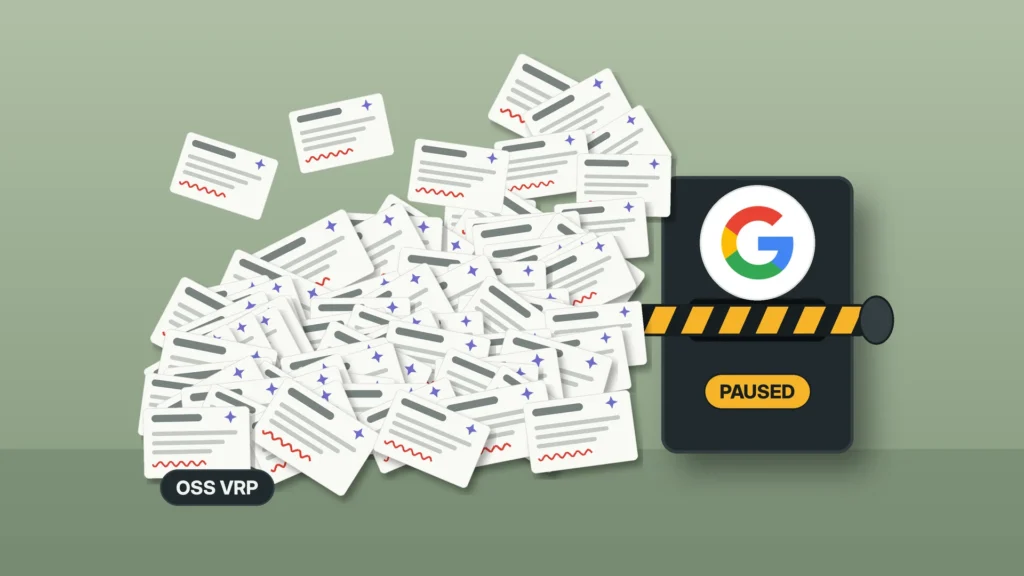
Google has stopped accepting product vulnerability reports to its Open Source Software Vulnerability Reward Program, citing a significant rise in automated submissions, most of them invalid. The pause took effect October 1, Google said in a post from its GoogleVRP account and on the program’s rules page. TechCrunch and The Verge tied the flood to AI-generated reports.
“This pause is due to a significant rise in automated submissions, the vast majority of which are not valid,” Google said. The company said it will “continue to reformat and work on this aspect of the OSS VRP” and committed to an update in the first quarter of 2027.
The freeze covers product vulnerabilities in Google’s open source code. Supply chain reports are not affected, and neither are product vulnerability reports submitted before October 1, according to Google. It may still accept some product vulnerability reports through its Cloud VRP for Google Cloud repositories that affect Cloud products, Tom’s Hardware reported. Google is steering researchers to its other reward programs and to its Patch Rewards Program, which pays up to $15,000 for high-impact fixes, BleepingComputer reported.
Google launched the OSS VRP in August 2022 to pay researchers who privately report flaws in projects it maintains, including Go, Angular, Bazel and Protocol Buffers, with rewards from $100 to $31,337. Across all its vulnerability reward programs, Google has paid researchers more than $81.6 million since 2010, including a record $17.1 million in 2025, according to BleepingComputer.
Google engineers and open source maintainers were overwhelmed by reports that were invalid or described hallucinated bugs, and validating them by hand pulled time away from fixing real vulnerabilities, Tom’s Hardware reported.
Google is not the first to pull back. In January, the maintainer of curl ended the project’s HackerOne bug bounty after a stream of AI slop reports, and in mid-September Intel removed financial rewards from its Intigriti bug bounty program without giving a reason, BleepingComputer reported.
The same tools are also finding real flaws. Last month a security startup used a modified free open model to find open source bugs that reached a TikTok user’s phone camera in a controlled demo, and Linux maintainers have said they were “completely overwhelmed” after AI-powered bug hunters pushed the kernel to a record number of vulnerabilities, Tom’s Hardware reported.